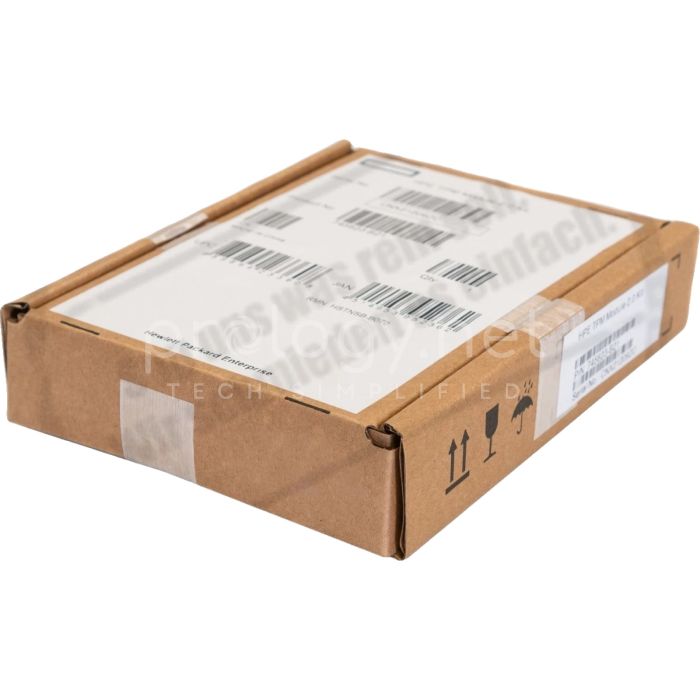
HPE 812119-001 745821-001 TPM 2.0 Trusted Platform Module
In Stock
1 units available
SKU
812119-001-NEW
MPN
812119-001
A$383.00
A$348.18
The HPE 812119-001 is a Trusted Platform Module (TPM) designed to enhance server security by providing hardware-based root of trust. This specific unit supports the TPM 2.0 specification, ensuring robust cryptographic capabilities for data protection. It integrates seamlessly with HPE server platforms to facilitate secure boot processes, measured boot, and platform integrity verification. By offloading cryptographic operations to dedicated hardware, it helps safeguard sensitive keys and credentials against software-based attacks and physical tampering.
In Stock
Brand
HPE
Type
Trusted Platform Module
Part Number
812119-001
Alternate Part Number
745821-001
Specification
TPM 2.0
Function
Hardware Security
Request a quote or add to cart — pricing available on enquiry for refurbished stock.
For international customers, please contact us for personalised support and assistance.
180-Days Warranty
Secure Checkout
Free Delivery AU
Dispatch in 1–2 Business Days
812119-001
HPE 812119-001 745821-001 TPM 2.0 Trusted Platform Module NEW
The HPE 812119-001 is a Trusted Platform Module (TPM) designed to enhance server security by providing hardware-based root of trust. This specific unit supports the TPM 2.0 specification, ensuring robust cryptographic capabilities for data protection. It integrates seamlessly with HPE server platforms to facilitate secure boot processes, measured boot, and platform integrity verification. By offloading cryptographic operations to dedicated hardware, it helps safeguard sensitive keys and credentials against software-based attacks and physical tampering.
This HPE Trusted Platform Module provides hardware-based security features essential for modern server environments. It supports the TPM 2.0 standard to ensure strong cryptographic performance and platform integrity.
Key Features
- Supports TPM 2.0 specification for enhanced security
- Provides hardware-based root of trust for platform integrity
- Facilitates secure boot and measured boot processes
- Protects sensitive cryptographic keys and credentials
- Integrates seamlessly with HPE server platforms
- Offloads cryptographic operations to dedicated hardware
- Helps safeguard against software-based attacks
- Ensures compliance with industry security standards
Documents
Product information is automatically compiled from trusted manufacturers and data providers. Please. report any errors.
| General | |
|---|---|
| Brand | HPE |
| Part Number | 812119-001 |
| Alternate Part Number | 745821-001 |
| Technical | |
| Specification | TPM 2.0 |
| Type | Trusted Platform Module |
| Function | Hardware Security |
Write Your Own Review
No FAQs available for this product yet.
No documents available for this product yet.